
External product security officer
External product security officer: your point of contact for the Cyber Resilience Act
Who answers the CRA questions from your customers, auditors and group headquarters, and who keeps the remediation plan together? Blackfort Technology takes on this coordination as an external product security officer, sometimes called a product security manager, here limited to cybersecurity under the CRA; general product safety under the German ProdSG and the GPSR is not covered. It is meant for mid-sized manufacturers that need steady CRA coordination but do not want to build their own product security team. You get a named, reachable point of contact from the Blackfort Technology team who gives you a substantive reply within four hours during our business hours, Monday to Friday. The responsibility under the Regulation stays with you; we do the groundwork.
What a CRA point of contact is for
The Cyber Resilience Act brings questions from several directions at once. Customers want to know what they will receive per product and per release, an audit asks for evidence, and group headquarters wants a status. Meanwhile, development is working through measures from the gap analysis that someone has to prioritise and follow up. Without one place where this comes together, decisions can stall.
The reporting obligations under Article 14 have applied since 11 September 2026; the remaining manufacturer obligations apply from 11 December 2027. A fixed point of contact keeps the overview across that period and gives consistent answers to the outside.
What the external product security officer covers
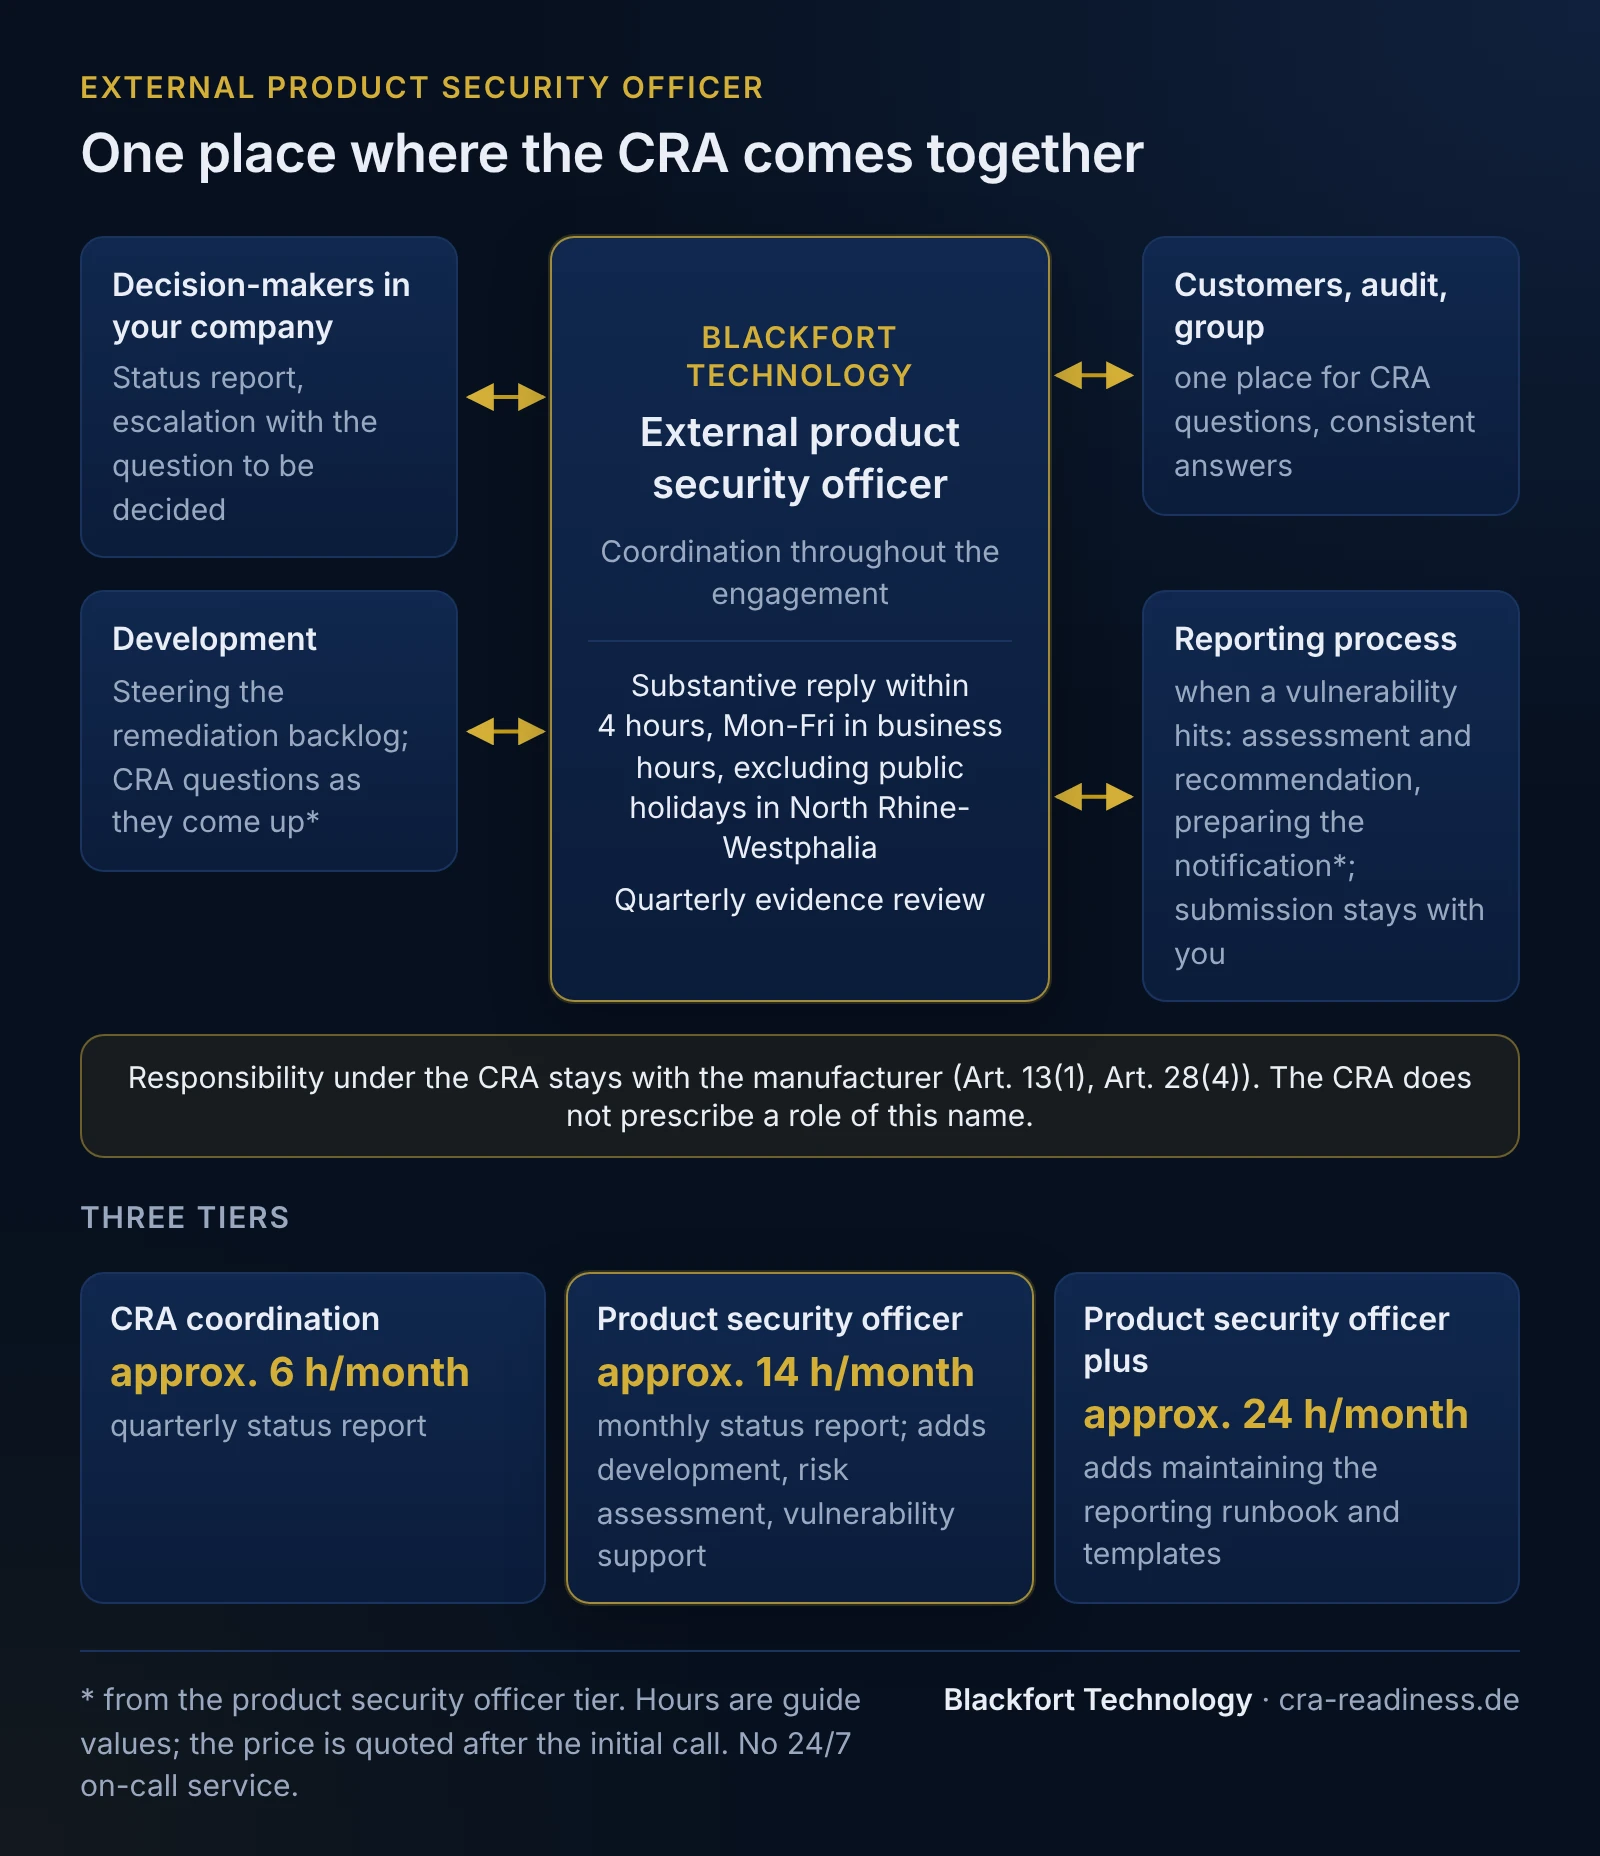
The coordination runs throughout the engagement. The tier table shows which services each tier includes.
One contact for CRA questions
For CRA questions from your customers, their audit and your group headquarters. Requests arrive in one place and get consistent answers. The single point of contact for users under Article 13(17) remains with your company.
Steering the remediation backlog
Measures from the gap analysis and the risk assessment are prioritised, tracked and agreed with the responsible teams.
CRA gap analysisQuestions from development
Your development teams get answers to CRA questions as they come up, for example on Annex I requirements, updates or documentation.
Status report
Monthly or quarterly depending on the tier: state of the measures, open items and what comes next.
Quarterly evidence review
Do technical documentation, risk assessment, SBOM and reporting process still match the current release? A short report with actions.
Support when a vulnerability hits
During business hours: assessment, a recommendation on whether to report and preparation of the early warning and notification. You decide whether to report; submission and technical analysis stay with you.
Reporting process and PSIRTEscalation
Where a decision is needed, we put it to the responsible person on your side, together with the question to be decided.
What you get
A named, reachable CRA point of contact from our team from day one.
01
One place for CRA requests
Customers, audit and group know whom to contact.
02
A managed backlog
Prioritised measures with ownership, across all products in the programme.
03
Substantive reply within four hours
Monday to Friday during business hours, for every request within the engagement.
04
Evidence reviewed quarterly
A short quarterly report on whether your CRA evidence still matches the current release. This is not a certification.
05
Clear decision paths
Open questions reach the people who have to decide them.
Who does what
Where the line runs between your company and the external point of contact, with a few examples:
| Task | Your company | Blackfort Technology |
|---|---|---|
| Responsibility for product compliance | Rests with the manufacturer (Art. 13(1), Art. 28(4)) | Supports implementation and evidence |
| Drawing up the EU declaration of conformity | Yes | No |
| Submitting notifications under Article 14 | Yes | Supports assessment and preparation |
| Answering CRA questions from customers, audit, group | Sets the line and decides | Day-to-day point of contact |
| Steering the remediation backlog | Implements the measures | Prioritises, tracks, reports |
We support the role and can act for it in working meetings, for example in an audit. We do not assume the obligation itself.
Three tiers
Every tier includes a substantive reply within four hours (Monday to Friday) and a quarterly evidence review. They differ in the monthly hour allowance and in how closely we support development and vulnerability cases.
| Service | CRA coordination | Product security officer | Product security officer plus |
|---|---|---|---|
| Hour allowance per month | approx. 6 hours | approx. 14 hours | approx. 24 hours |
| Point of contact for customers, audit and group | ✓ | ✓ | ✓ |
| Steering the remediation backlog | ✓ | ✓ | ✓ |
| Status report | quarterly | monthly | monthly |
| Review of the CRA evidence | quarterly | quarterly | quarterly |
| Substantive reply within four hours, Mon-Fri | ✓ | ✓ | ✓ |
| CRA questions from development as they come up | - | ✓ | ✓ |
| Coordinating the risk assessment per product | - | ✓ | ✓ |
| Support when a vulnerability hits | - | ✓ | ✓ |
| Attending audit and customer meetings | - | within the allowance | within the allowance |
| Maintaining the reporting runbook and templates | - | - | ✓ |
We quote the price in our proposal after a free initial call. The hours are guide values. Replies to requests count towards the allowance; the proposal fixes the allowance and what happens to unused hours. Effort beyond the allowance as agreed. Reply time: Monday to Friday during our business hours, excluding public holidays in North Rhine-Westphalia, you receive a substantive reply within four hours; the proposal states the business hours, and time outside them does not count. If a full answer takes longer, that reply tells you when to expect it. No 24/7 on-call service.
How we start
The first steps of the engagement.
1
Free initial call
Products, customers, existing roles and implementation status. You then receive a proposal with a clearly defined scope.
2
Agree roles
Who decides on your side, which requests come to us, how we appear towards customers and audit.
3
Take over the backlog
From an existing gap analysis or from an inventory we carry out with you.
4
Ongoing coordination
Answer requests, track measures, report, review the evidence quarterly, put decisions forward.
Your contact
Christian Gebhardt · Founder and managing director, Blackfort Technology
Christian Gebhardt, founder and managing director of Blackfort Technology, is happy to take your enquiry personally. In a free initial call you work out together what you need; the consulting is carried out by the Blackfort Technology team.
Does the CRA require a product security officer?
No. The Cyber Resilience Act does not establish a mandatory role called product security officer. Its obligations fall on the manufacturer, who must ensure that the product has been designed, developed and produced in accordance with the essential cybersecurity requirements of Annex I Part I (Article 13(1)) and who, by drawing up the EU declaration of conformity, assumes responsibility for compliance (Article 28(4)). Whether you give a person or function the coordinating role is your decision.
Two other terms need to be kept apart. The single point of contact under Article 13(17) is a channel through which users communicate directly and rapidly with the manufacturer and report vulnerabilities; it belongs in the information and instructions to the user (Annex II(2)). A manufacturer may appoint an authorised representative under Article 18 by written mandate; the obligations of Article 13(1) to (11), among others, cannot form part of that mandate. Acting as authorised representative is not part of our service.
When a vulnerability hits
In the Product security officer and Product security officer plus tiers, if an actively exploited vulnerability or a severe incident becomes known, we help you assess it during business hours: is the vulnerability actively exploited (Article 3(42)), is the incident severe (Article 14(5)), and which notification may be due? You receive the result as a recommendation; we prepare the early warning and the notification with you. Cases that remain legally open are flagged for your legal department or counsel.
Technical analysis and remediation stay with your development team, and submission via the single reporting platform stays with you. Because the early warning is due without undue delay and at the latest 24 hours after you become aware, nights and weekends included, your company needs its own reachable role for it. We can build that process with you.
Beyond the conformity assessment
The obligations do not end with CE marking. Vulnerabilities must be handled throughout the support period (Article 13(8)), the reporting obligations continue, and the technical documentation must be kept up to date (Article 31(2)). The role is therefore set up for the long term and runs for as long as the engagement does.
In every tier we review your CRA evidence once a quarter: do technical documentation, risk assessment, SBOM and reporting process still match the current release? You receive a short report with the actions needed for the backlog.
Point of contact and implementation from one provider
If you want to hand over CRA implementation as a whole, the coordination can be combined with the other modules: inventory and gap analysis, risk assessment and threat model per product, SBOM and vulnerability management, the Article 14 reporting process, technical documentation and user information. The point of contact keeps the backlog together across all products.
The aim is security evidence that an auditor or customer can follow: gap report, risk assessment, SBOM per release, a documented reporting process and documentation per product. For the information security of the organisation, for example within the ISMS, Blackfort Technology offers the same model as an external information security officer: https://www.blackfort-tec.de/en/external-information-security-officer
What we do not do
So that expectations are right:
- We do not take over the manufacturer obligations: responsibility under the CRA stays with your company.
- No legal services: questions that need a legal decision are flagged for review by your legal department or counsel.
- We are not a notified body and issue neither certificates nor attestations.
- You submit Article 14 notifications yourself; technical analysis and remediation stay with your development team.
- Reply time: Monday to Friday during our business hours, excluding public holidays in North Rhine-Westphalia, you receive a substantive reply within four hours; the proposal states the business hours, and time outside them does not count. If a full answer takes longer, that reply tells you when to expect it. No 24/7 on-call service.
- Penetration tests are not part of our services.
The CRA obligations remain with your company. We help you meet them and document the evidence.
Frequently asked questions
Is a product security officer mandatory under the CRA?+
No. The Regulation places the obligations on the manufacturer and leaves internal organisation to it. What is required is the single point of contact for users under Article 13(17), for example for vulnerability reports; it does not replace internal coordination.
Do you take over our CRA obligations?+
No. The responsibility the Regulation places on the manufacturer stays with your company; by drawing up the EU declaration of conformity, the manufacturer assumes responsibility for compliance. We support the role and can act for it in working meetings, for example in an audit. We do not assume the obligation itself.
Can we commission the entire CRA implementation from you?+
Yes. The modules from gap analysis to technical documentation can be commissioned together or individually, with coordination running alongside. We clarify what you need in the initial call.
What does an external CRA point of contact cost?+
There are three tiers with a monthly allowance of roughly 6, 14 or 24 hours. Which one fits depends on the number of products, customers with their own requirements and how far your implementation has come. We quote the price in our proposal after a free initial call.
How quickly do you reply?+
Monday to Friday during our business hours, excluding public holidays in North Rhine-Westphalia, you receive a substantive reply within four hours, in every tier; the proposal states the business hours. We do not offer a 24/7 on-call service; for the Article 14 early warning, which is due without undue delay and at the latest 24 hours after you become aware, nights and weekends included, your company needs its own reachable role.
Does the support end with CE marking?+
No. Vulnerability handling, reporting obligations and keeping the technical documentation up to date continue throughout the support period. The role is set up for the long term, with a quarterly evidence review.
Further reading
- Manufacturer obligations under the CRA
- CRA roles at a glance
- Building the reporting process and PSIRT
- CRA workshop
- CRA consulting: all services
This content provides general technical and organizational information on the Cyber Resilience Act (Regulation (EU) 2024/2847) and does not constitute legal advice (no legal services within the meaning of the German RDG).
Last updated: 2026-10-09
Get in touch
Request a CRA point of contact
Tell us about your products, your customers and where your implementation stands. The initial call is free and without obligation; we usually reply to your enquiry within one to two working days. The four-hour reply time applies once the engagement has started.