
Last updated: 2026-10-09
Anyone placing products with digital elements from a non-EU manufacturer on the Union market is an importer under the Cyber Resilience Act (CRA, Regulation (EU) 2024/2847, Art. 3(16)) - and thus a gatekeeper. Its role under Art. 19 is to ensure that only conforming products reach the EU market. This page provides a technical-organisational orientation on importer duties. It offers guidance, not binding individual advice; a legal assessment in the specific case remains reserved for legal counsel.
The key point up front
The importer is the last filter before the EU market. It may place only conforming products on the market and must ensure that the manufacturer has done its homework: conformity assessment carried out, technical documentation drawn up, CE marking affixed. What the importer explicitly does not do: carry out the conformity assessment itself, draw up the technical documentation, or affix the CE marking - these remain the manufacturer's duties alone.
Why the importer role exists
The CRA primarily addresses the manufacturer (Art. 13). Where that manufacturer sits outside the EU, however, the European market surveillance authorities lack a direct point of contact and a responsible party inside the Union. The importer closes exactly this gap: it is the economic operator established in the EU that places a product bearing the name or trademark of a manufacturer established outside the Union on the Union market. It therefore bears an independent responsibility for the gatekeeper function at market entry; responsibility for product design stays with the manufacturer. For how this differs from the other roles, see our roles overview (manufacturer, importer, distributor).
The verification duty: place only conforming products
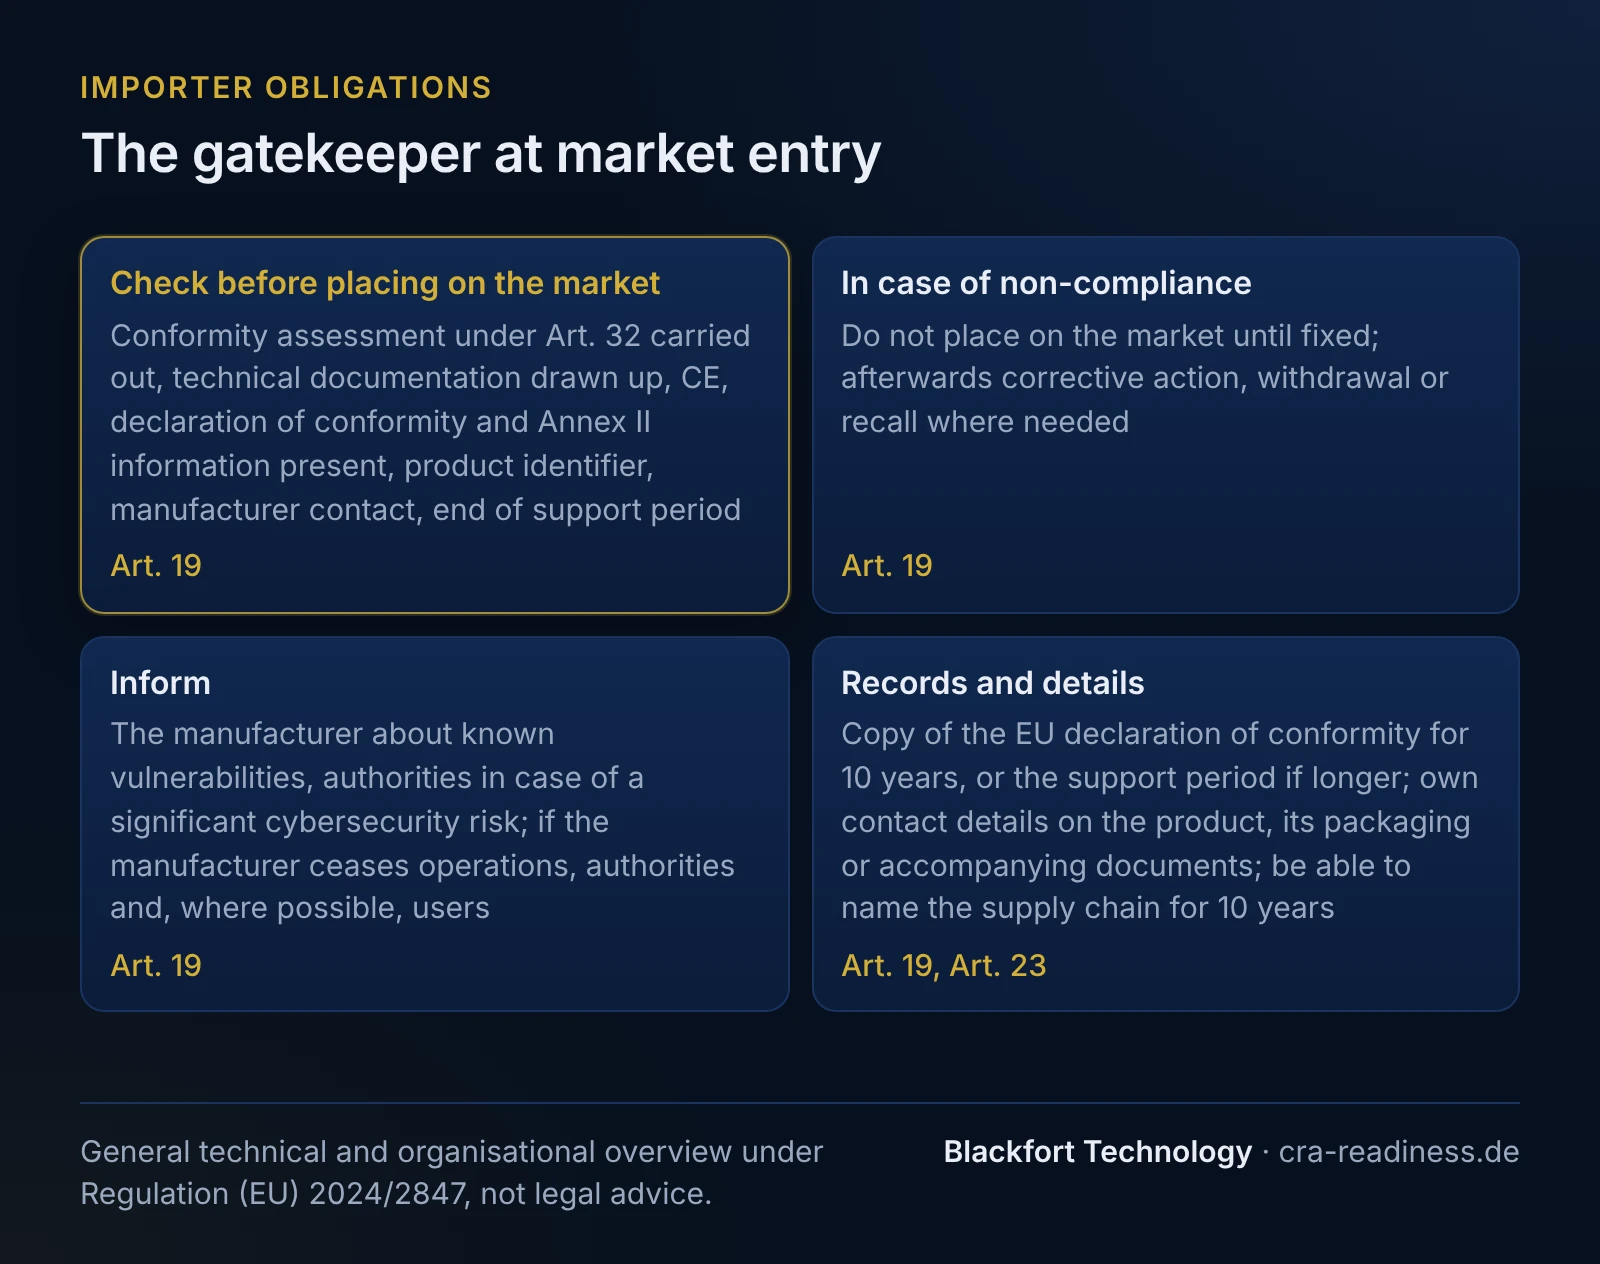
The core of the importer's duty under Art. 19 is that only conforming products are placed on the market (para. 1). Before an importer puts a product on the market, it ensures that the manufacturer has actually completed the central steps (para. 2):
- the conformity assessment was carried out under the relevant procedure (Art. 32),
- the manufacturer has drawn up the technical documentation (Annex VII),
- the product bears the CE marking and is accompanied by the EU declaration of conformity and the user information and instructions under Annex II in an easily understood language,
- the manufacturer has indicated the product identifier, its name and contact details and the end date of the support period (Art. 13(15), (16) and (19)).
The importer must be able to provide the documents proving this. This check is a verification, not a re-assessment: the importer does not re-evaluate whether the product meets the essential requirements of Annex I - it satisfies itself that the manufacturer's intended evidence and steps are in place. The substantive security responsibility remains with the manufacturer.
What the importer explicitly does NOT do
- It does not carry out the conformity assessment (that is a manufacturer duty under Art. 32).
- It does not draw up the technical documentation (that is a manufacturer duty under Annex VII).
- It does not affix the CE marking (that is a manufacturer duty under Art. 30).
If the importer places a product on the market under its own name or trademark, or substantially modifies a product already placed on the market, it is considered a manufacturer under Art. 21 and is subject to the obligations of Articles 13 and 14.
No placing on the market where non-conforming
Where the importer considers or has reason to believe that a product or the manufacturer's processes are not conforming, it must not place it on the market until conformity has been established (Art. 19(3)). This is not a matter of discretion: where the CE marking is missing, the conformity assessment has not been carried out, or the technical documentation is not available, market entry must not proceed until the product has been brought into conformity. Where the product presents a significant cybersecurity risk, it also informs the manufacturer and the market surveillance authorities. The importer must therefore actively prevent market entry.
Corrective action and escalation
If it emerges - including after the fact - that a product already placed on the market is not conforming, the importer immediately takes the necessary corrective action (Art. 19(5)). Depending on severity this ranges from bringing the product into conformity, through withdrawal from the market, to recall. Information duties apply in parallel:
- Where the importer becomes aware of a vulnerability in the product, it informs the manufacturer without undue delay.
- Where a product presents a significant cybersecurity risk, the importer additionally informs the market surveillance authorities of the Member States in which it made the product available immediately, giving details in particular of the non-compliance and of any corrective action taken.
- Where the importer becomes aware that the manufacturer has ceased its operations and can no longer meet its obligations, it informs the market surveillance authorities and, where possible, the users (Art. 19(8)).
An important clarification: the reporting deadlines under Art. 14 (early warning, notification, final report via the single reporting platform) are addressed to the manufacturer. The importer has no reporting obligation under Art. 14; it may report voluntarily under Art. 15. It passes its findings on to the manufacturer and the authorities.
Documentation and marking by the importer
Even though the importer does not draw up the technical documentation, it keeps a copy of the EU Declaration of Conformity at the disposal of the market surveillance authorities for at least ten years after placing on the market or for the support period, whichever is longer, and ensures it can make the technical documentation available to them on request (Art. 19(6)). In addition, it indicates its name, trade name or trademark, postal address and email address or other digital contact on the product, its packaging or in the accompanying documents (Art. 19(4)). This keeps the importer findable for authorities and users as the responsible actor within the EU. On request, it must also be able to tell the authorities for ten years from whom it obtained a product and, where available, to whom it supplied it (Art. 23).
Importer duties checklist (Art. 19)
The following checklist summarises the operational duties. It does not replace an individual assessment but serves as a starting point for an internal check-and-release procedure before placing on the market.
| Duty | Verification / action step |
|---|---|
| Only conforming products | Before placing on the market, ensure the product is CRA-conforming |
| Verify conformity assessment | Check that the manufacturer carried out the procedure under Art. 32 |
| Verify technical documentation | Check that the manufacturer drew up the documentation (Annex VII) |
| Check CE marking | Inspect the CE marking, the EU declaration of conformity and the information/instructions under Annex II |
| Check manufacturer information | Product identifier, manufacturer contact details, end date of the support period |
| Block non-conformity | Where conformity is missing, do not place on the market until fixed |
| Corrective action | On non-conformity: establish conformity, withdraw/recall if needed |
| Vulnerability → manufacturer | Report known vulnerabilities to the manufacturer without undue delay |
| Significant risk → authority | Inform market surveillance authorities of significant cybersecurity risk |
| Manufacturer ceases operations | Inform market surveillance authorities and, where possible, users |
| EU Declaration of Conformity | Keep a copy for ten years or the support period; be able to provide technical docs on request |
| Contact details | Indicate own contact details on the product, packaging or accompanying documents |
| Supply chain | Be able to name suppliers and customers for ten years (Art. 23) |
Penalty framework and distinction from the distributor
For infringements of importer duties, Art. 64(3) provides for fines of up to EUR 10 million or 2% of total worldwide annual turnover of the preceding financial year, whichever is higher. For infringements of Annex I and of Articles 13 and 14, Art. 64(2) sets the ceiling at EUR 15 million or 2.5%. Member States lay down the detailed rules on penalties.
The importer is to be distinguished from the distributor (Art. 20), which merely makes a product available in the supply chain without first placing it on the market from a third country. Its verification depth is lower - it acts with due care (including checking the presence of the CE marking) but owes no verification of the conformity assessment. Details in our article on the distributor duties. The applicability check gives a first orientation on whether your product is affected.
Note: These explanations are general technical-organisational information, not legal advice within the meaning of the German Legal Services Act (RDG). The specific allocation of roles and the resulting duties depend on the individual case and may change with Commission guidance.
Frequently asked questions
What is an importer under the CRA?+
Must an importer carry out the conformity assessment itself?+
What must an importer do if it discovers a vulnerability?+
What fine does an importer risk for breaches?+
How does the importer differ from the distributor?+
Sources
This content provides general technical and organizational information on the Cyber Resilience Act (Regulation (EU) 2024/2847) and does not constitute legal advice (no legal services within the meaning of the German RDG).