
EN 18031 and the Radio Equipment Directive
EN 18031 and the Radio Equipment Directive: cybersecurity for radio products
Since 1 August 2025, internet-connected radio products and several other device groups have had to meet the cybersecurity requirements of the Radio Equipment Directive (RED). Blackfort Technology helps you assess technically which products are affected, compares them with EN 18031 and prepares the risk assessment and documentation for the conformity assessment in a way you can reuse for the Cyber Resilience Act.
What the RED has required since August 2025
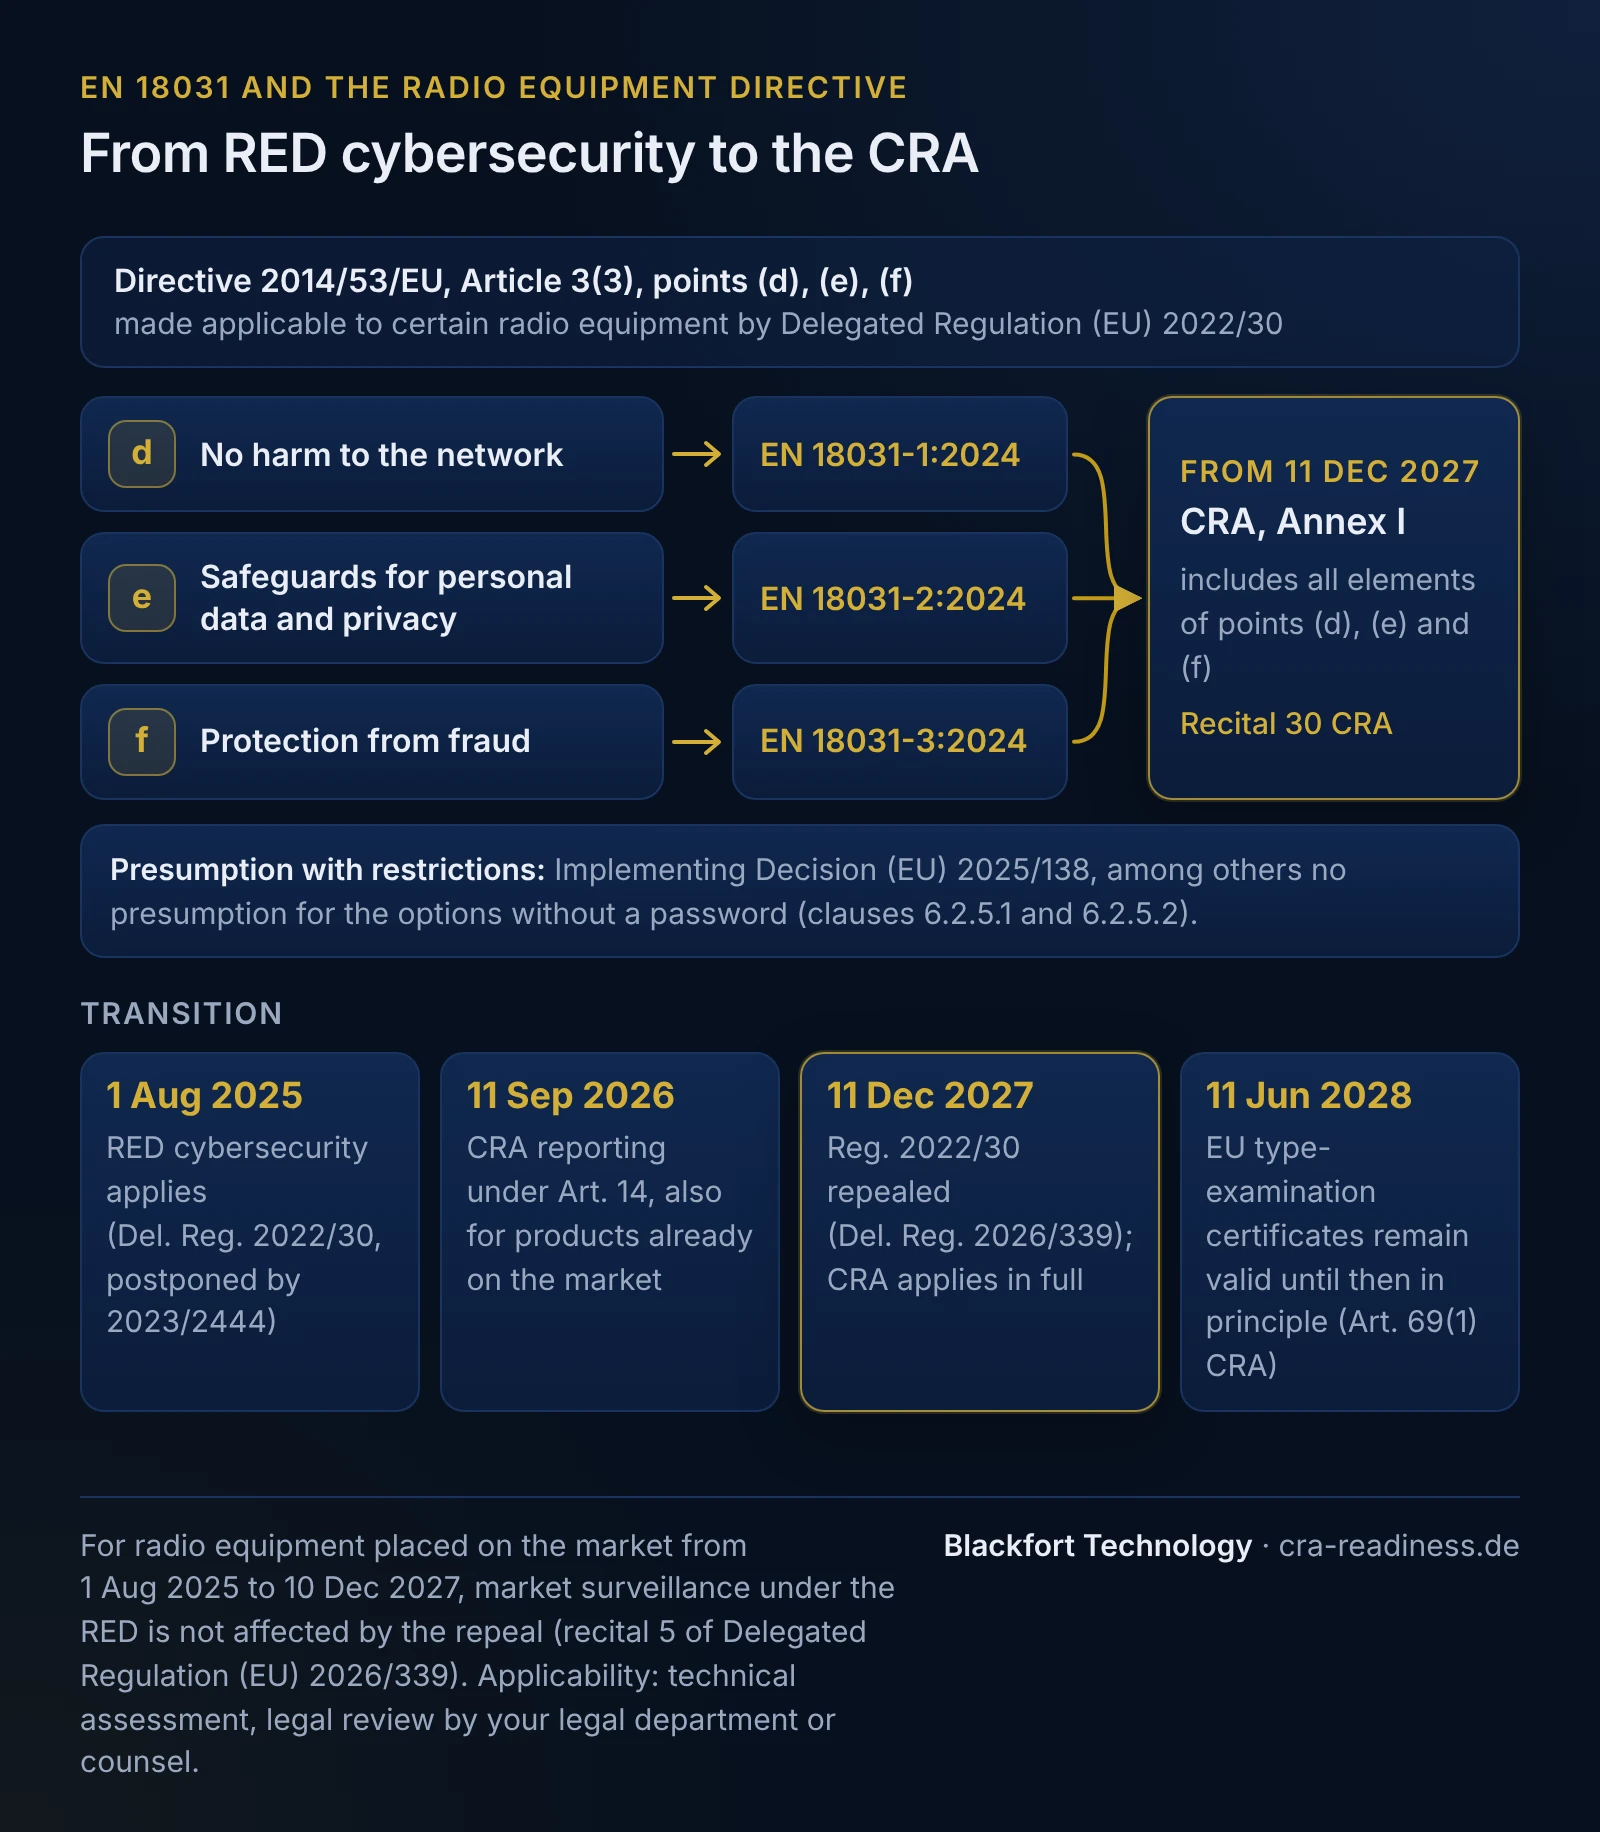
Delegated Regulation (EU) 2022/30 makes three essential requirements in Article 3(3) of Directive 2014/53/EU applicable to certain radio equipment: point (d), no harm to the network; point (e), safeguards for personal data and privacy; and point (f), protection from fraud. It has applied since 1 August 2025, postponed by Delegated Regulation (EU) 2023/2444.
Point (d) covers radio equipment that can itself communicate over the internet, directly or via other equipment. Point (e) covers such equipment as well as childcare radio equipment, radio toys and wearables, where they can process personal data, traffic data or location data. Point (f) covers internet-connected radio equipment that lets users transfer money, monetary value or virtual currency. Exclusions, for medical devices for instance, are set out in Article 2 of the Delegated Regulation.
Service modules
You commission what is missing. We build on your existing documentation and test reports.
Technical applicability assessment
A product inventory covering radio interfaces, internet connectivity, data and payment functions, and for each product a technical assessment of points (d), (e) and (f), flagged for review by your legal department or counsel.
Radio equipment and the CRAGap analysis against EN 18031
Comparison with EN 18031-1, -2 or -3 based on architecture, documentation and interviews. We flag where a restricted option is involved, such as operation without a password.
Risk assessment and threat model
Architecture, data flows and trust boundaries derived from source code and configuration, with the threat model kept as code in your repository and re-runnable on a changed release.
Threat modelingDocumentation for the conformity assessment
The cybersecurity parts of the technical documentation under Article 21 and Annex V RED, such as the list of standards applied or solutions adopted, plus the risk analysis and assessment that Annex III, Module B, point 3(c) requires for EU-type examination.
Bridge to the CRA
We map the results to Annex I CRA and list what is still missing there, such as the SBOM and the reporting process.
CRA gap analysisWhat you end up with
Results for the technical documentation that remain useful under the CRA.
01
RED product register
For each product, a technical assessment of points (d), (e), (f) with reasons, plus the legal questions flagged for review by your legal department or counsel.
02
EN 18031 gap report
Rated findings, a prioritised action plan, the places where the presumption is restricted.
03
Documented risk assessment
For the technical documentation, with a model that runs again on a changed release.
04
RED to CRA mapping
What you can carry over to Annex I CRA and what is still missing.
How we work
From a product list to documentation an assessor can follow.
1
Free initial call
Your radio products and the state of your documentation. You then receive a proposal with a clearly defined scope.
2
Applicability
Record the product inventory, assess points (d), (e), (f) per product from a technical standpoint, flag legal questions.
3
Gap analysis
Compare one reference product with EN 18031, rate findings, prioritise actions.
4
Risk assessment and documentation
Build the threat model, document the risk assessment, compile the documentation.
5
Roll out and prepare for the CRA
Apply the method to further products, map the results to the CRA requirements.
Your contact
Christian Gebhardt · Founder and managing director, Blackfort Technology
Christian Gebhardt, founder and managing director of Blackfort Technology, is happy to take your enquiry personally. In a free initial call you work out together what you need; the consulting is carried out by the Blackfort Technology team.
EN 18031: presumption of conformity with restrictions
The Commission published EN 18031-1:2024 (point (d)), EN 18031-2:2024 (point (e)) and EN 18031-3:2024 (point (f)) in the Official Journal by Implementing Decision (EU) 2025/138, with restrictions. No presumption of conformity is conferred by the sections named "rationale" and "guidance", in all three parts by the options in clauses 6.2.5.1 and 6.2.5.2 that allow the user not to set and use any password, in EN 18031-2 where parental access control for toys and childcare equipment is missing, and in EN 18031-3 by the assessment criteria for secure updates in clause 6.3.2.4.
If you apply the standards, you may choose internal production control, EU-type examination or full quality assurance (Article 17(3) RED). If they are not applied or applied only in part, the options are EU-type examination or full quality assurance, both involving a notified body (Article 17(4)). For EU-type examination, the technical documentation must include an adequate analysis and assessment of the risks (Annex III, Module B, point 3(c)).
What changes with the Cyber Resilience Act
Delegated Regulation (EU) 2026/339 repeals Regulation 2022/30 with effect from 11 December 2027, the date from which the Cyber Resilience Act applies in full. According to recital 30, its essential cybersecurity requirements include all elements of points (d), (e) and (f). For radio equipment placed on the market from 1 August 2025 to 10 December 2027, market surveillance under the RED is not affected by the repeal (recital 5 of Delegated Regulation (EU) 2026/339).
For radio products within the scope of the CRA, the reporting obligations under Article 14 have applied since 11 September 2026, including for products already on the market (Article 69(3)). Under Article 69(1), EU type-examination certificates on cybersecurity issued under other Union legislation generally remain valid until 11 June 2028. The risk assessment and documentation you build for EN 18031 now can serve as a starting point for the risk assessment under Article 13 and the technical documentation under Annex VII CRA.
What we do not do
So that expectations are right:
- We are not a test laboratory and do not test your devices. Penetration testing is not part of our services.
- We are not a notified body and do not issue certificates of any kind. You, as the manufacturer, draw up the EU declaration of conformity.
- No legal services: questions that need a legal decision are flagged for review by your legal department or counsel.
The obligations under the Radio Equipment Directive and the CRA remain with your company. We help you meet them and document the evidence.
Frequently asked questions
Since when have the RED cybersecurity requirements applied?+
Since 1 August 2025. The original date was 1 August 2024; Delegated Regulation (EU) 2023/2444 postponed it.
Is a device affected if it only talks to a smartphone over Bluetooth?+
Point (d) also covers radio equipment that can communicate over the internet via other equipment. Whether that applies depends on the architecture. We assess it technically and flag the legal question for review by your legal department or counsel.
Is applying EN 18031 enough?+
Only as far as the presumption of conformity extends, and Implementing Decision (EU) 2025/138 restricts it. Where the standards are not applied or applied only in part, Article 17(4) RED requires a procedure involving a notified body.
Is the work worth it if the Regulation is repealed in 2027?+
Until 10 December 2027 the obligation applies to every affected product you place on the market. After that, the risk assessment and documentation can serve as a starting point for the Article 13 risk assessment and the Annex I requirements of the CRA.
Do you test our devices?+
No. We are not a test laboratory, and penetration testing is not part of our services.
Further reading
- CRA and radio equipment: delineation from the RED Delegated Act
- Conformity assessment and CE marking under the CRA
- Risk assessment and threat modeling
- The CRA for IoT and embedded
- Technical documentation and conformity
This content provides general technical and organizational information on the Cyber Resilience Act (Regulation (EU) 2024/2847) and does not constitute legal advice (no legal services within the meaning of the German RDG).
Last updated: 2026-10-09
Get in touch
Request EN 18031 consulting
Tell us about your radio products and the state of your documentation. The initial call is free and without obligation.